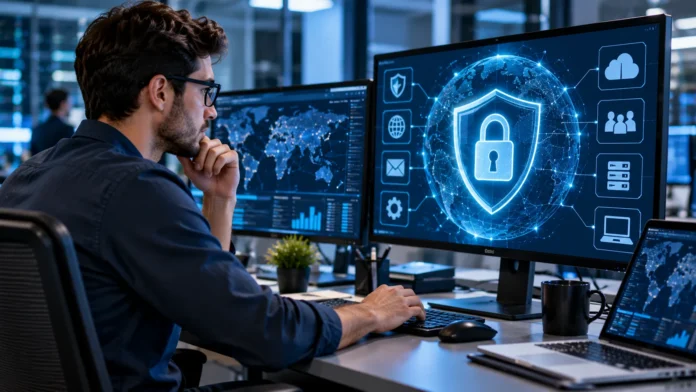

Cybersecurity has become an essential part of modern digital life because individuals, businesses, and governments depend heavily on connected technologies. From online banking and cloud storage to business communication and digital payments, sensitive information moves across computer networks every day. Protecting these systems from unauthorized access, cyberattacks, and data breaches is the central purpose of cybersecurity.
Many people understand that cybersecurity involves protecting computers, but its responsibilities extend much further. It includes safeguarding personal information, maintaining reliable technology services, preventing unauthorized changes to data, and ensuring digital systems remain available when needed. These objectives help organizations maintain trust, protect operations, and reduce the risks associated with digital threats.
Understanding what cybersecurity is primarily concerned with provides a foundation for learning about information security, network protection, cyber risk management, and modern defense strategies. This guide explores the core objectives of cybersecurity, common threats, essential technologies, and practical security principles. It also explains why cybersecurity matters for businesses, individuals, and organizations operating in an increasingly connected world.
What Is Cybersecurity Primarily Concerned With?
Cybersecurity is primarily concerned with protecting digital systems, networks, devices, applications, and information against unauthorized access, attacks, damage, and disruption. Its central objective is to reduce the likelihood and impact of cyber threats while helping authorized users access technology safely. Cybersecurity combines technical safeguards, organizational policies, and responsible user practices.
The three fundamental goals of cybersecurity are confidentiality, integrity, and availability, collectively known as the CIA triad. Confidentiality protects information from unauthorized disclosure, integrity helps ensure data remains accurate and trustworthy, and availability ensures systems and information can be accessed when required. Together, these principles guide many security decisions across different industries.
Cybersecurity also involves identifying potential threats, managing vulnerabilities, detecting suspicious activity, and responding effectively to security incidents. Organizations must continuously evaluate their systems because attackers, technologies, and business requirements change over time. Effective cybersecurity therefore focuses on ongoing risk management rather than assuming that one security product can prevent every possible attack.
Understanding the CIA Triad in Cybersecurity
The CIA triad is a foundational information security model used to explain the primary objectives of cybersecurity. It consists of confidentiality, integrity, and availability, which represent three important characteristics of protected information and systems. Security strategies often balance these objectives according to organizational needs, operational requirements, and the potential consequences of security failures.
Confidentiality focuses on restricting access to sensitive information, while integrity concerns the accuracy and reliability of that information. Availability ensures that authorized users can access systems and services when needed. A security incident may affect one or several of these objectives, depending on the attack method and the systems involved.
For example, a data breach can compromise confidentiality, unauthorized modifications can undermine integrity, and a service outage can affect availability. Understanding these differences helps organizations identify appropriate safeguards. The CIA triad also provides a useful framework for evaluating security risks and explaining technical protection goals to nontechnical audiences.
Confidentiality: Protecting Sensitive Information
Confidentiality is concerned with preventing unauthorized individuals or systems from accessing private or sensitive information. Businesses regularly handle customer records, employee information, financial documents, and confidential operational data. Protecting these resources helps maintain privacy, support legal obligations, and reduce the potential consequences of information exposure.
Common confidentiality safeguards include access controls, encryption, secure authentication, and appropriate information-sharing policies. Organizations can restrict sensitive records to employees who require them for legitimate responsibilities. Encryption also helps protect information from unauthorized reading when it is stored or transmitted, provided that encryption keys are managed securely.
Confidentiality depends on both technology and everyday behavior. Employees must recognize suspicious requests, follow information-handling procedures, and avoid sharing sensitive data through inappropriate channels. Regular training and clearly defined access permissions help organizations reduce accidental disclosures while strengthening protection against intentional attempts to obtain confidential information.
Integrity: Keeping Data Accurate and Trustworthy
Integrity refers to maintaining the accuracy, consistency, and completeness of information throughout its intended use. Cybersecurity aims to prevent unauthorized or unintended modifications that could make data unreliable. This objective is particularly important for financial transactions, business records, healthcare information, and systems where incorrect information may influence significant decisions.
Organizations use safeguards such as access restrictions, audit logs, cryptographic checks, and controlled update procedures to support data integrity. These mechanisms help identify unexpected changes and limit who can modify important records. Backups and version histories may also help restore trustworthy information when accidental changes or security incidents occur.
Integrity involves more than preventing deliberate cyberattacks. Software errors, human mistakes, and technical failures can also damage important information. By maintaining reliable data management practices, organizations support accurate reporting, dependable operations, and greater confidence in the digital information used for everyday business activities.
Availability: Ensuring Systems Remain Accessible
Availability means keeping digital systems, networks, applications, and information accessible to authorized users when required. Businesses depend on reliable technology to communicate, process transactions, deliver services, and support daily operations. When essential systems become unavailable, organizations may experience financial losses, operational delays, and reduced customer confidence.
Cybersecurity threats such as distributed denial-of-service attacks and ransomware can disrupt system availability. Equipment failures, configuration mistakes, and environmental incidents may also cause interruptions. Organizations therefore use monitoring, backup systems, redundancy, and recovery planning to reduce the likelihood and duration of service disruptions.
Effective availability planning considers which services are most important and how quickly they must be restored following an incident. Organizations may establish recovery objectives and test their procedures regularly. These practices help maintain operational resilience while recognizing that no digital infrastructure can guarantee uninterrupted service under every circumstance.
Protecting Computer Networks From Cyber Threats
Network security is a major cybersecurity concern because connected systems exchange information across internal networks and the internet. Attackers may attempt to exploit network vulnerabilities, intercept communications, or gain unauthorized access to connected devices. Protecting network infrastructure helps reduce these risks and supports reliable communication between authorized users and services.
Common network protection technologies include firewalls, intrusion detection systems, secure communication protocols, and network monitoring tools. Organizations may also divide networks into separate segments to limit unnecessary access between systems. These controls work together to manage traffic, identify suspicious behavior, and reduce the potential impact of security incidents.
Network protection requires ongoing maintenance because infrastructure and threats evolve. Security teams review configurations, install appropriate updates, and monitor activity for unusual patterns. Combining technical safeguards with clear administrative responsibilities helps organizations maintain safer network environments without assuming that any single defensive technology provides complete protection.
Data Security and Information Protection
Data security focuses on protecting digital information throughout its lifecycle, including collection, storage, processing, sharing, and disposal. Organizations manage many forms of data, from customer contact details to internal business records. Each category may require different levels of protection depending on sensitivity and operational importance.
Important data security practices include encryption, secure storage, backup management, and controlled access. Data classification policies help employees understand which information requires additional safeguards. Organizations should also consider how long records need to be retained and how they can be disposed of securely when no longer required.
Strong data security supports broader business and privacy objectives. It helps reduce unauthorized disclosure, accidental loss, and inappropriate modifications. Regular assessments can identify weaknesses in information-handling processes and support improvements as technologies, data volumes, and organizational responsibilities change.
Preventing Unauthorized Access to Systems
Controlling access is one of cybersecurity’s most important responsibilities because many attacks involve attempts to use accounts or systems without permission. Unauthorized access can expose confidential information, allow harmful changes, or disrupt essential services. Organizations therefore need reliable methods for identifying users and limiting their permissions.
Authentication verifies a user’s claimed identity, while authorization determines which resources that user can access. Strong authentication methods, including multifactor authentication, can provide additional protection against account compromise. Access policies should also follow the principle of least privilege, giving users only the permissions necessary for their responsibilities.
Account security requires regular attention as employees change roles, leave organizations, or receive new responsibilities. Unused accounts and excessive permissions can introduce unnecessary risks. Periodic access reviews, secure account recovery processes, and monitoring help maintain appropriate control over digital resources.
Cybersecurity Threats and Common Attack Types
Cybersecurity is concerned with understanding threats that may compromise systems, information, or business operations. Common threats include phishing, malware, ransomware, credential theft, and attacks targeting software vulnerabilities. These threats differ in their methods, but they can affect confidentiality, integrity, availability, or several security objectives simultaneously.
Phishing attempts often use deceptive communication to persuade recipients to disclose information or interact with malicious content. Malware refers to software designed to perform harmful or unauthorized actions. Ransomware can interfere with access to systems or data, creating serious operational challenges for affected organizations.
Threat awareness helps organizations prioritize suitable defenses rather than reacting only after incidents occur. Security teams consider likely attack methods, exposed assets, and potential business consequences. A risk-based approach allows organizations to concentrate resources on threats most relevant to their environment and responsibilities.
Application Security and Software Protection
Application security focuses on protecting software against vulnerabilities, unauthorized activity, and misuse. Modern businesses rely on websites, mobile applications, cloud services, and internal software to deliver essential functions. Weaknesses in these applications can expose information, affect system reliability, or create opportunities for unauthorized access.
Secure software development incorporates security considerations throughout planning, coding, testing, deployment, and maintenance. Development teams may use code reviews, dependency management, automated testing, and vulnerability assessments. These practices help identify weaknesses before they become serious problems in production environments.
Application security also requires attention after software is released. New vulnerabilities may emerge as technologies and attack methods evolve. Regular updates, appropriate monitoring, and coordinated vulnerability management help maintain protection while allowing applications to continue supporting changing business requirements.
Cloud Security and Digital Infrastructure
Cloud security addresses the protection of information, applications, and services hosted through cloud computing environments. Organizations increasingly rely on cloud platforms for storage, collaboration, and business operations. These systems offer flexibility but also introduce security considerations involving configuration, identity management, and access to shared resources.
Cloud providers and their customers typically share security responsibilities, although the exact division depends on the service model. Providers may manage certain infrastructure protections, while customers remain responsible for areas such as user permissions, data handling, and application configuration. Understanding these responsibilities helps prevent security gaps caused by incorrect assumptions.
Cloud security practices include strong authentication, appropriate access controls, encryption, monitoring, and configuration reviews. Organizations should also evaluate backup arrangements and service continuity requirements. A carefully managed cloud environment can support secure operations when security responsibilities are clearly defined and consistently maintained.
Endpoint Security and Device Protection
Endpoint security focuses on protecting devices that connect to organizational networks and services. These devices include laptops, desktop computers, smartphones, tablets, and servers. Because endpoints are commonly used to access business information, compromised devices may provide opportunities for attackers to interfere with operations or access sensitive resources.
Endpoint protection can involve security software, device encryption, system updates, and controlled application permissions. Organizations may also use centralized device management to maintain consistent security configurations. These safeguards help reduce exposure to common threats while allowing employees to perform legitimate work across different environments.
Remote and hybrid working arrangements make endpoint security particularly important. Employees may access organizational services from multiple locations and network connections. Clear device policies, strong authentication, and regular maintenance help organizations manage these risks without unnecessarily restricting productive work.
Cyber Risk Management and Vulnerability Assessment
Cyber risk management involves identifying potential security problems and evaluating their likelihood and possible consequences. Not every vulnerability creates the same level of risk, so organizations must prioritize their responses. This process helps security teams allocate resources to the systems and threats that matter most.
Vulnerability assessments identify weaknesses in software, devices, and configurations that could expose systems to attacks. Security teams evaluate the findings and determine suitable corrective actions. Risk prioritization may consider technical severity, exposure, business importance, and whether a weakness is being actively exploited.
Effective risk management is continuous because digital environments change as organizations introduce new technologies and services. Regular reviews help identify emerging concerns and verify that existing controls remain appropriate. This approach supports informed decisions while recognizing that cybersecurity aims to manage risk rather than eliminate every possible threat.
Incident Detection and Cybersecurity Response
Cybersecurity also focuses on identifying suspicious activity and responding effectively when security incidents occur. Even organizations with strong preventive measures can experience attacks or technical failures. Detection and response capabilities help limit the impact of these events and support the restoration of affected services.
Security teams may use monitoring systems, event logs, and alerting tools to identify unusual behavior. An incident response plan establishes responsibilities and procedures for assessing and managing security events. Clear communication between technical teams and organizational leadership can support coordinated decisions during disruptions.
After an incident, organizations should review what happened and identify opportunities to improve their safeguards. Lessons learned may lead to updated security procedures, better monitoring, or additional training. Preparing in advance helps reduce confusion and enables a more organized response when unexpected security problems occur.
Importance of Cybersecurity Awareness and Training
Human behavior plays an important role in cybersecurity because employees regularly interact with email, applications, passwords, and sensitive information. Mistakes or deceptive messages can create security risks even when technical protections are present. Awareness training helps people recognize potential threats and understand their responsibilities.
Effective cybersecurity education covers topics such as phishing recognition, secure account practices, responsible information sharing, and incident reporting. Training should use relevant examples and clear language rather than overwhelming participants with technical terminology. Regular reinforcement can help employees apply security principles during everyday activities.
A positive security culture encourages people to report suspicious activity and ask questions when uncertain. Organizations should make reporting processes accessible and avoid discouraging employees from raising concerns. Combining supportive education with appropriate technical controls creates a stronger foundation for protecting digital environments.
Cybersecurity Best Practices for Businesses and Individuals
Cybersecurity best practices begin with understanding which information, accounts, and devices require protection. Businesses should maintain an inventory of important systems and establish clear responsibilities for managing them. Individuals can also benefit from recognizing which online accounts contain personal or financial information.
Common protective measures include using unique passwords, enabling multifactor authentication, installing security updates, and maintaining suitable backups. Keeping applications and operating systems current helps address known vulnerabilities. These practices reduce common security risks, although their effectiveness depends on consistent implementation and appropriate system configuration.
Organizations should also review access permissions, train employees, and prepare for possible service disruptions. Individuals can protect themselves by checking suspicious messages carefully and avoiding unnecessary disclosure of personal information. Combining several practical safeguards provides more reliable protection than depending on a single security measure.
Conclusion
Cybersecurity is primarily concerned with protecting digital information, computer systems, applications, and networks from unauthorized access, harmful activity, and disruption. Its core objectives are confidentiality, integrity, and availability, commonly represented by the CIA triad. These principles provide a foundation for understanding how organizations protect sensitive information and maintain reliable digital operations.
Modern cybersecurity includes multiple areas of protection, such as network security, application security, cloud security, endpoint protection, and identity management. Threat detection, risk assessment, and incident response also contribute to effective defense. Each area addresses different challenges while supporting the broader goal of managing digital security risks.
As technology continues to evolve, cybersecurity requires ongoing attention from businesses, governments, and individual users. Strong authentication, regular updates, employee awareness, and appropriate security policies can reduce common risks. Understanding cybersecurity’s primary concerns helps people make informed decisions and contribute to safer digital environments.
Frequently Asked Questions (FAQs)
What is cybersecurity primarily concerned with?
Cybersecurity is primarily concerned with protecting information, devices, networks, and digital systems from unauthorized access, attacks, and disruption. Its three fundamental objectives are maintaining confidentiality, integrity, and availability.
What are the three main goals of cybersecurity?
The three main goals are confidentiality, integrity, and availability. These principles help ensure information remains protected from unauthorized disclosure, stays accurate and trustworthy, and remains accessible to authorized users.
Why is cybersecurity important for businesses?
Cybersecurity helps businesses protect sensitive information, maintain operations, and reduce risks associated with cyberattacks. Effective safeguards also support customer trust, regulatory responsibilities, and business continuity.
What is the difference between cybersecurity and information security?
Cybersecurity focuses on protecting digital systems, networks, and information against cyber threats. Information security has a broader scope that includes protecting information in both digital and physical forms.
What are the most common cybersecurity threats?
Common cybersecurity threats include phishing, malware, ransomware, credential theft, and attacks exploiting software vulnerabilities. Their potential effects include data exposure, unauthorized modifications, account compromise, and service disruption.